AI promises speed. But can your organisation explain who is accountable when it gets something wrong? That is the question to bring to #RISK Expo Europe 2026, taking place on 10–11 November at ExCeL London.
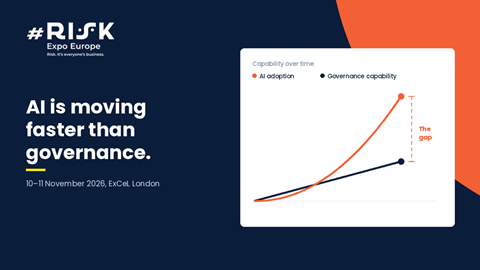
A new report from AXA XL and cyber security consultancy S-RM warns that AI is becoming embedded in critical business processes faster than many organisations can adapt their governance, security and incident-response capabilities.
The challenge is not simply whether to adopt AI. It is whether the business can scale its use without losing sight of responsibility, exposure and control.
For leaders responsible for risk, compliance, security, privacy and resilience, that should be a prompt for action, not a reason to put innovation on hold.
Join the conversation at #RISK Expo Europe 2026, 10–11 November at ExCeL London.
- Come with the questions your organisation has not yet resolved.
- Compare approaches with peers.
- Challenge providers on how their solutions work in practice.
- Hear from subject matter experts
Use the conversations to identify what needs to change in your own business.
Bring a colleague from another function.
A conversation about AI accountability is more valuable when the people responsible for the technology, the controls and the business consequences can challenge the same assumptions together.
Join the conversation at #RISK Expo Europe 2026, 10–11 November at ExCeL London.
Sessions on AI accountability across all three stages:
Tuesday 10 November
- 10:00 | GRC Stage — Risk Is Our Business: The Future of GRC. Michael Rasmussen, GRC 20/20, opens with responsible AI governance and connected accountability
- 11:20 | #RISK Stage — AI and Cloud Concentration Risk: The Governance Questions Boards Can No Longer Defer. Vendor concentration, shadow AI, and the liability questions landing on the audit committee’s desk
- 12:50 | BFSI Stage — AI in the Three Lines of Defence. Where automation strengthens the model, and where it creates dependencies risk, audit and compliance must govern jointly. In partnership with RiskSmart
Wednesday 11 November
- 10:00 | PrivSec AI Governance — Agentic AI and the Death of the Static Data Inventory, with Michael Charles Borrelli, AI & Partners, on governing systems that don’t sit still
- 10:30 | GRC Stage — Translating Ethical AI Governance Into the Operating Model. Arcangelo Leone de Castris, Aviva, and Jack Saunders, Trident, on who owns AI governance day to day
- 10:30 | PrivSec AI Governance — keynote from Lord Chris Holmes, author of the Artificial Intelligence (Regulation) Bill
- 11:10 | PrivSec AI Governance — AI vs AI: Cyber Threats, Defences and the Governance Gap Between Them
- 11:20 | GRC Stage — AI-Enabled GRC: Use Cases, Limits and Guardrails. Ian Rae, John Lewis Partnership, and Lorraine Pinter, Arsenal Football Club
- 12:50 | PrivSec AI Governance — Shadow AI and the Extended Vendor Chain: Auditing Third-Party AI Tools and Sub-Processors
- 13:40 | GRC Stage — Who Actually Approved the AI? Eleonor Duhs, Partner, Marks & Clerk, on what a court wants reconstructed after the fact
- 13:40 | PrivSec AI Governance — keynote from Max Schrems, founder of noyb
1 Reader's comment